Now PRO on development
Lewis John Villamor
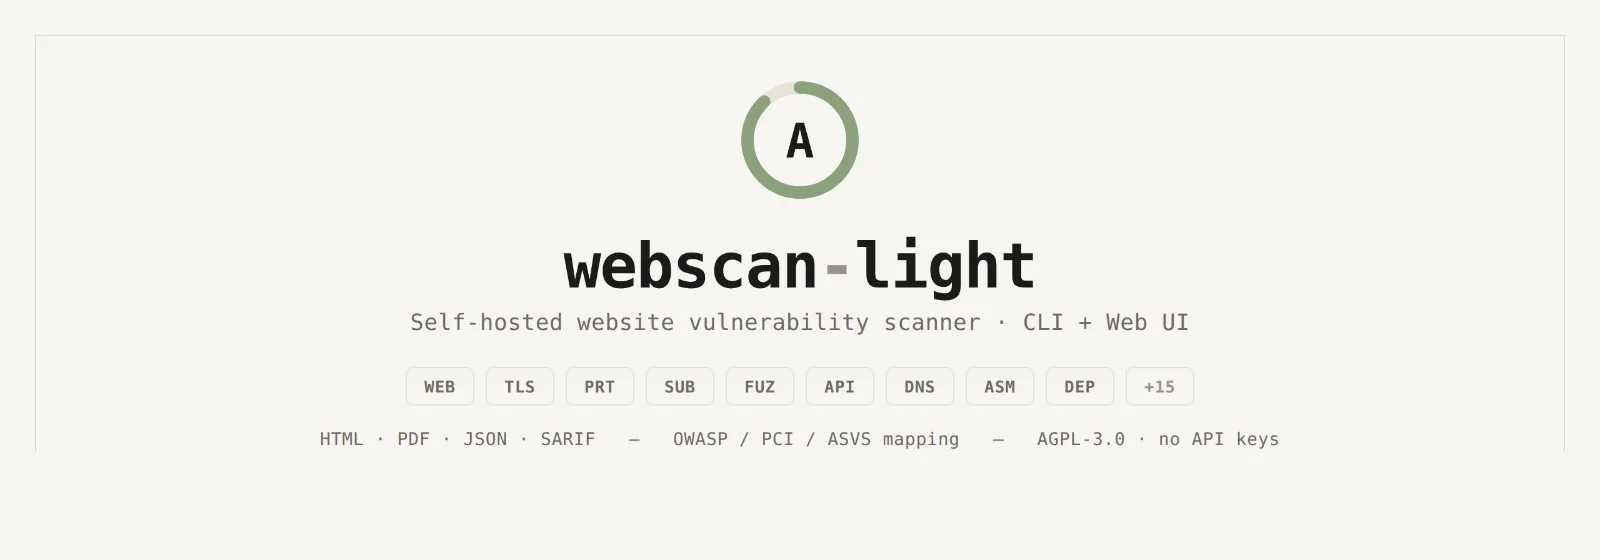
Free, self-hosted web vulnerability scanner suite (CLI + UI) that generates pentest-style reports. Authorized use only.
Made by
@lewis-john-villamor
Full Stack Developer / Solutions Architect
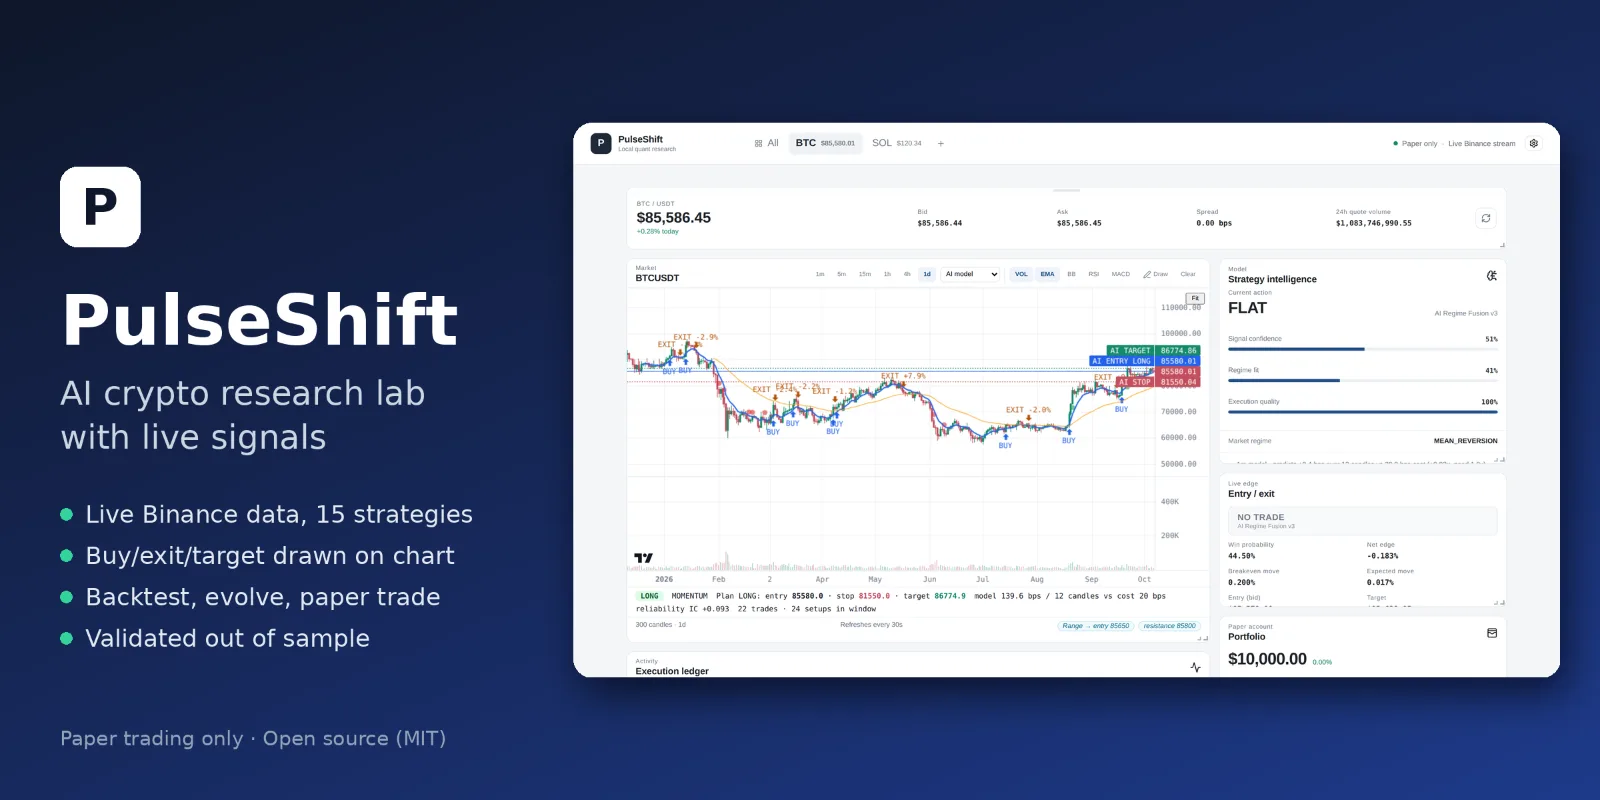
PulseShift
Open-source crypto lab that draws AI buy/sell signals on live charts. Paper only.
Live
Kemdara
Cryptography Workbench
Building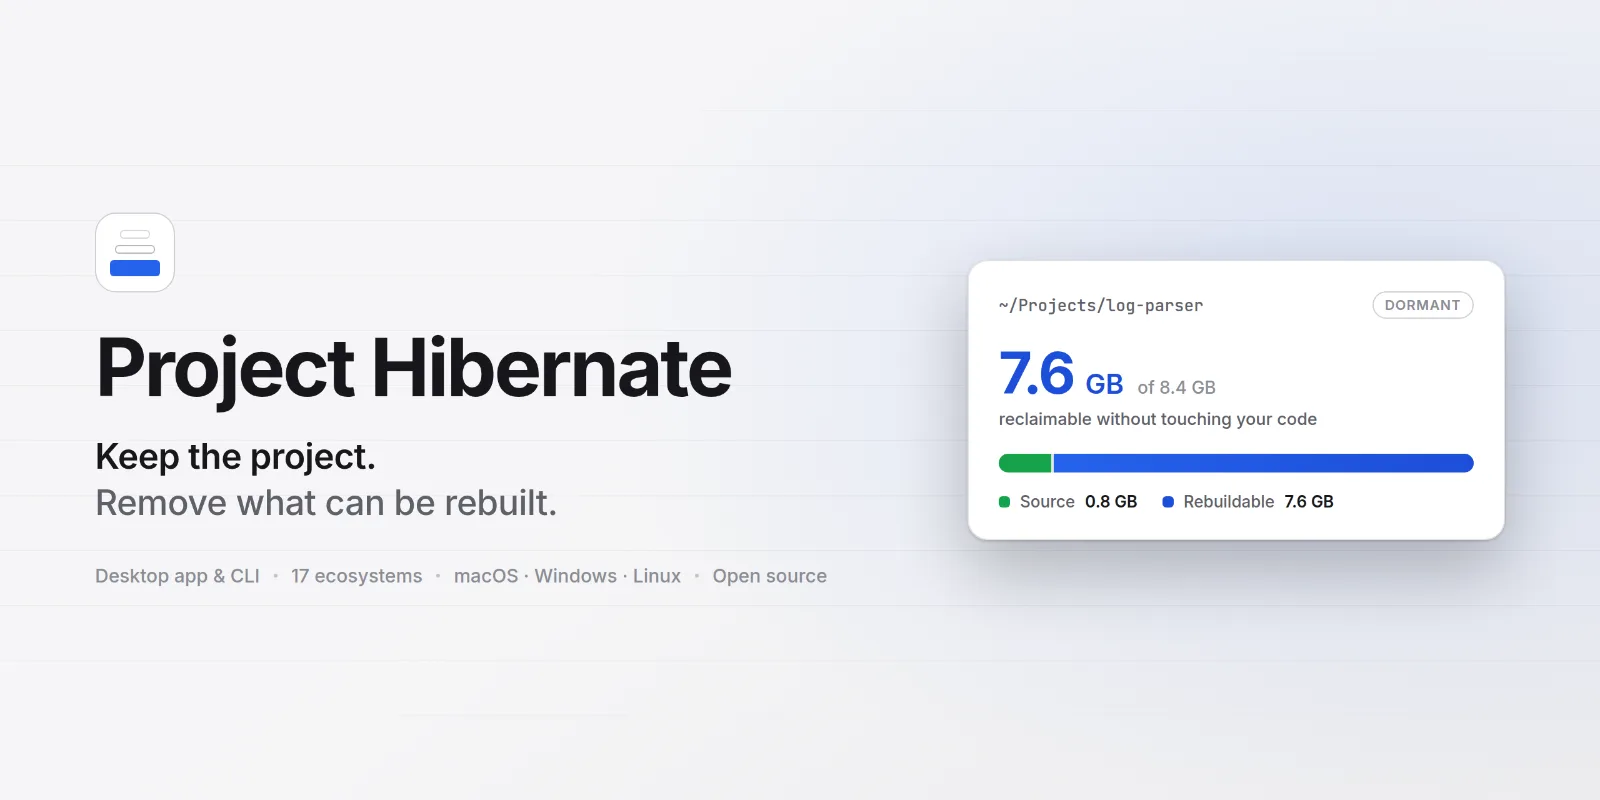
Project Hibernate
Local desktop app that reclaims disk space from dormant dev projects by removing rebuildable artifacts, never source cod
Live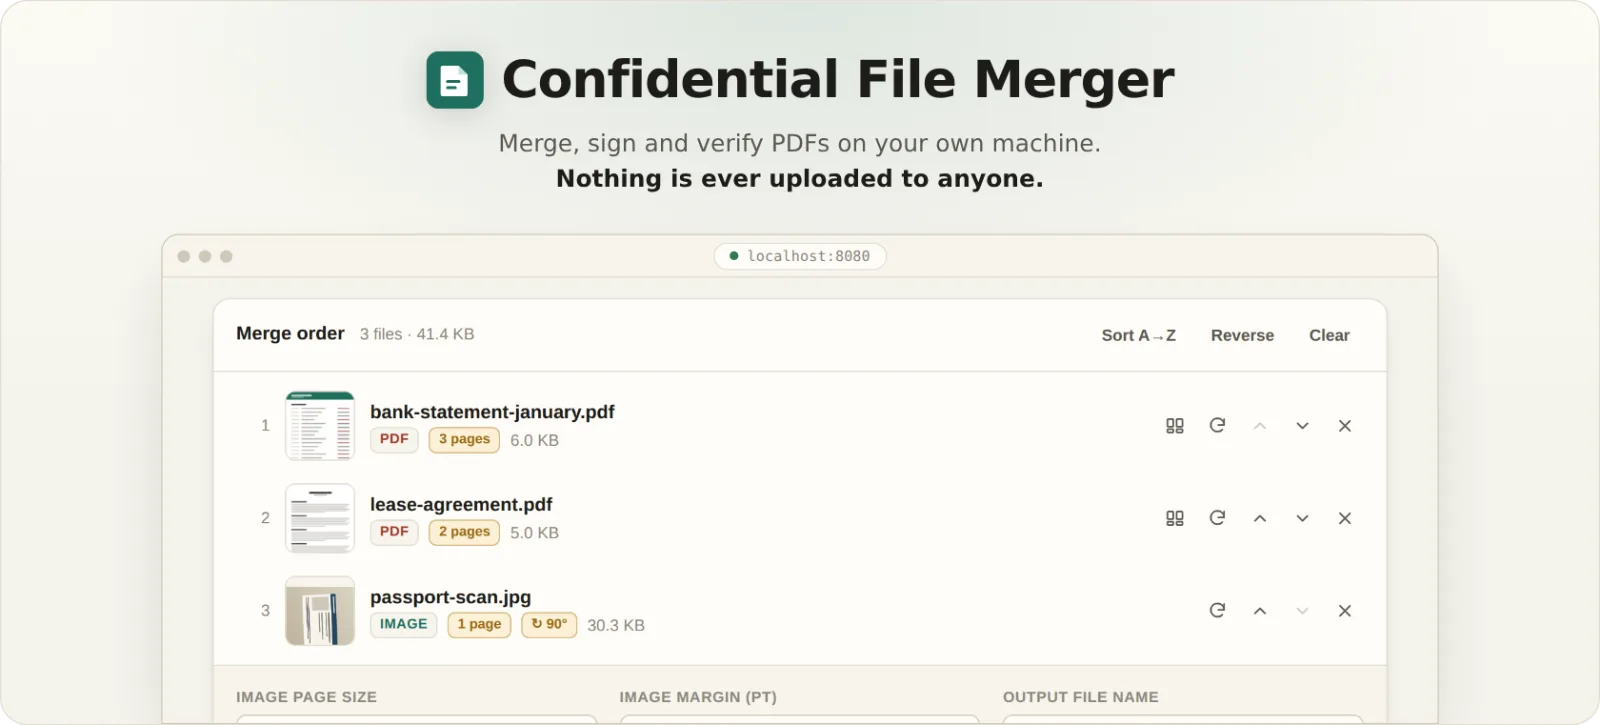
Confidential File Merger
Merges PDFs and images into one PDF on your own machine. Self-hosted, fully offline, nothing ever leaves your computer.
LiveLewis John Villamor
Now PRO on development
Lewis John Villamor
Updates:
Code Security Scan (code) — point at a folder: supply-chain/npm-poisoning heuristics (typosquats, install scripts, non-registry deps, missing integrity), lightweight SAST, IaC/config checks, and secrets — one report.
UI upload flow — code/secrets/deps now scan an uploaded project .zip in a deleted-after sandbox (Zip-Slip + zip-bomb guards); server disk never read.
robots.txt-aware crawling (--respect-robots) + CSV export (-f csv).
Web hardening — security response headers + /robots.txtThis file is outside this session’s folders, so it can’t be opened here..
Product-shot banner (real UI screenshots).
Lewis John Villamor
If you need help securing your app, I’d be happy to help. Feel free to reach out!
Lewis John Villamor
Will soon release a paid version of this app.
Lewis John Villamor
Updates:
Small improvements added to webscan-light
Security response headers — new SecurityHeadersMiddleware sets X-Content-Type-Options: nosniff, X-Frame-Options: DENY, Referrer-Policy: no-referrer, Cross-Origin-Opener-Policy, and a minimal Permissions-Policy on every web-UI response. A scanner now holds itself to the standards it reports on.
/robots.txtThis session isn’t running, so its files can’t be opened. Send a message to start it again. — disallows indexing so an accidentally-exposed self-hosted instance won't be crawled; reachable without auth/consent.
Tests — added coverage for both; 98 tests pass, ruff clean, bandit 0 issues.
Lewis John Villamor
Practical use cases for Webscan Light Pentest
Small businesses checking their own websites for common security issues
Developers testing apps before deployment
Students learning practical web security in a controlled environment
Freelancers auditing client websites with permission
Internal IT teams reviewing company-owned websites and APIs
Self-hosters checking VPS, homelab, and exposed services
Monitoring subdomains, ports, certificates, and attack-surface changes
Checking dependencies for known vulnerabilities
Generating pentest-style reports for remediation and documentation
Built for defenders, developers, learners, and small teams that want a free, self-hosted security toolkit.
Authorized use only — scan systems you own or have explicit permission to test.
Lewis John Villamor
Ethical Use
webscan-light is built for defenders and learners — to find and fix weaknesses, not to break in.
Get permission first. Only scan systems you own or have explicit written authorization to test. Unauthorized scanning is illegal in many places.
Do no harm. Active checks send real payloads; run them only on non-production or approved targets. Keep scans gentle.
Disclose responsibly. If you find a vulnerability that isn't yours, report it privately to the owner — don't exploit or publish it.
Learn, don't weaponize. Findings are for understanding and remediation.
You are responsible for how you use this tool. Use it to make the web safer.
Lewis John Villamor
Website vulnerability scan — 40+ named checks producing PentestTools-style reports (severity, EPSS, CVE, remediation)
24 tools: SSL/TLS, port & network scan, subdomain/vhost finder, URL fuzzer, web recon, API scanner, Google dorks, subdomain takeover, cloud & secrets, dependency (OSV) scan, typosquat, ASM
Injection suite (authorized): XSS, SQLi, SSTI, command injection, LFI, stored XSS — detect + safe PoC only
JS-rendered crawling via headless Chromium for SPA-aware discovery
Authenticated scanning — cookie, header, or form login
Attack Surface Monitor with host screenshots and change alerts
Reports — minimalist HTML/PDF with SVG gauges, grades, OWASP/PCI/ASVS mapping; JSON + SARIF export
Server UI + CLI — run scans, browse history, schedule recurring monitors, webhook/email alerts
Safety — authorization gating, consent, SSRF/scope guard, rate limiting, caching
Self-hosted — SQLite persistence, Docker image, AGPL-3.0, stdlib-first Python
Building a dev tool or hiring developers? Get seen here. Become our Sponsor
Building a dev tool or hiring developers? Get seen here. Become our Sponsor